
Study & Preparation
Claude Security Explained for CCDV-F Certification
About this video
A system prompt can guide Claude’s behavior—but it cannot enforce permissions, protect secrets, or prevent unauthorized actions. In this video, we break down Claude application security for CCDV-F certification preparation and real-world enterprise AI architecture. We’ll explore why reliable AI security requires multiple independent control layers around the model, from identity verification and context protection to tool authorization and operational monitoring. Topics covered include: Why prompts are not security boundaries Designing trust boundaries around Claude applications Minimizing sensitive data before it reaches the model Separating secrets, credentials, and application logic Defending against prompt injection and untrusted content Building multi-stage guardrail pipelines Securing Claude Code workflows with permissions and hooks Preparing incident response and containment strategies A critical engineering principle is understanding that model output is only a proposal. Before any real-world effect occurs, your application must validate, authorize, and constrain the action. We’ll examine a layered security approach: Authenticate the caller Minimize the context sent to the model Validate model responses Authorize tool execution Isolate runtime capabilities Monitor and respond to abnormal behavior For CCDV-F preparation, focus on the security question behind every scenario: Which boundary failed, and which deterministic control should prevent the next failure? Secure Claude applications are not built by making the model perfectly obedient. They are built by designing systems where a model mistake cannot become an uncontrolled system action. #Claude #CCDVF #ClaudeCertification
Keep watching
 6:31
Study & Preparation
Claude Certified Developer Foundations CCDV-F Certification Overview
 7:40
Study & Preparation
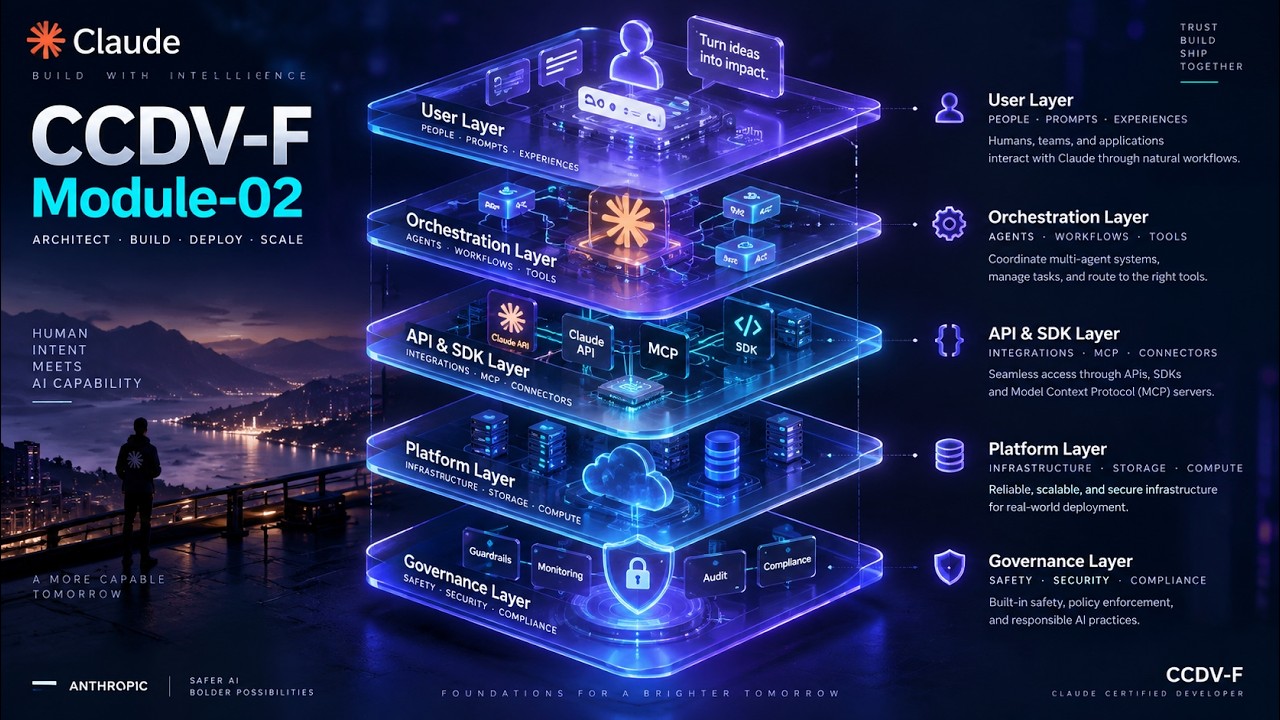
Claude Application Systems Life Cycle Explained | CCDV-F Certification
 7:39
Study & Preparation
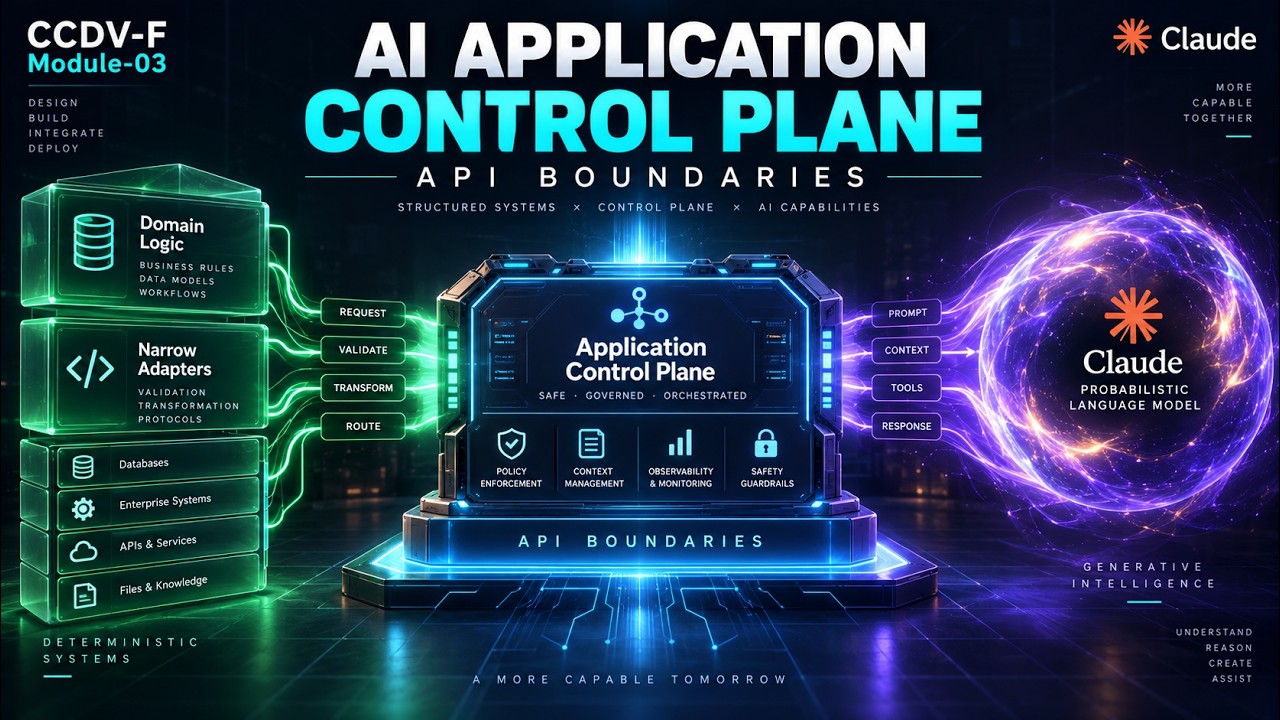
Claude Application Architecture Explained | CCDV-F AI Boundaries
 7:19
Study & Preparation
Claude Messages API Foundations Explained for CCDV-F Exam Preparation
 9:11
Study & Preparation
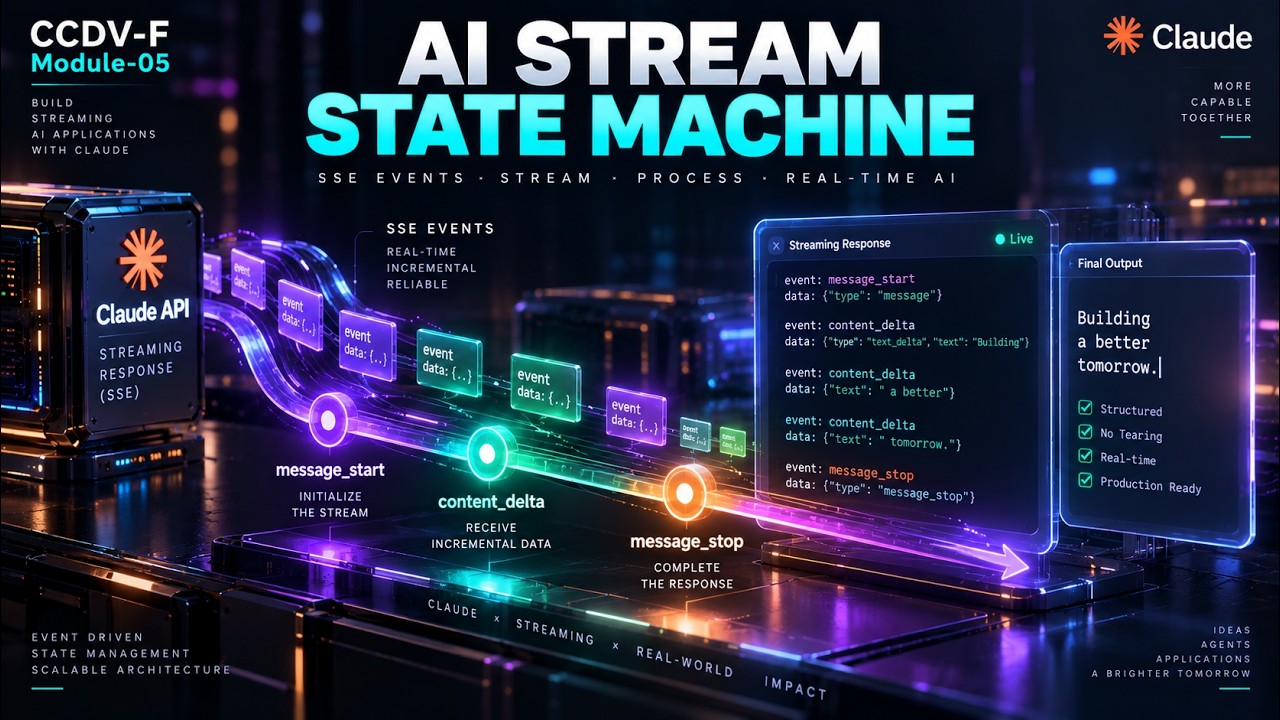
Claude API Streaming Explained for CCDV-F Certification
 9:47
Study & Preparation