
Study & Preparation
3V0-24.25 VCF 9.0 Harbor Registry and CA Trust Explained
About this video
Preparing for the VMware 3V0-24.25 VCF 9.0 Architect Exam requires understanding how Kubernetes workloads securely consume private images. In this video, we analyze one of the most common enterprise deployment failures: Pods entering an ImagePullBackOff state because of an x509: certificate signed by unknown authority error. You will learn how VKS handles private registry integration, including: Harbor deployment as a VKS Standard Package Carvel package management concepts Enterprise Root CA trust configuration The difference between certificate trust failures and credential failures Kubernetes registry secrets and namespace boundaries ServiceAccount-based imagePullSecrets configuration Image pull verification and troubleshooting workflows A common exam mistake is immediately changing registry credentials when the real problem is certificate trust. The 3V0-24.25 exam tests whether you understand the order of operations: Establish certificate trust Configure registry authentication Validate workload image pulls We will walk through the troubleshooting logic behind private registry failures and show how architects should analyze image distribution problems in a VCF environment. By the end of this module, you will have a practical framework for securing container image pipelines and diagnosing Harbor integration issues. Next, we will move higher into the application security layer and explore Istio Service Mesh, mTLS, and modern zero-trust traffic management. #3V0-2425 #VCF9 #VMwareCertification
Keep watching
 7:07
Study & Preparation
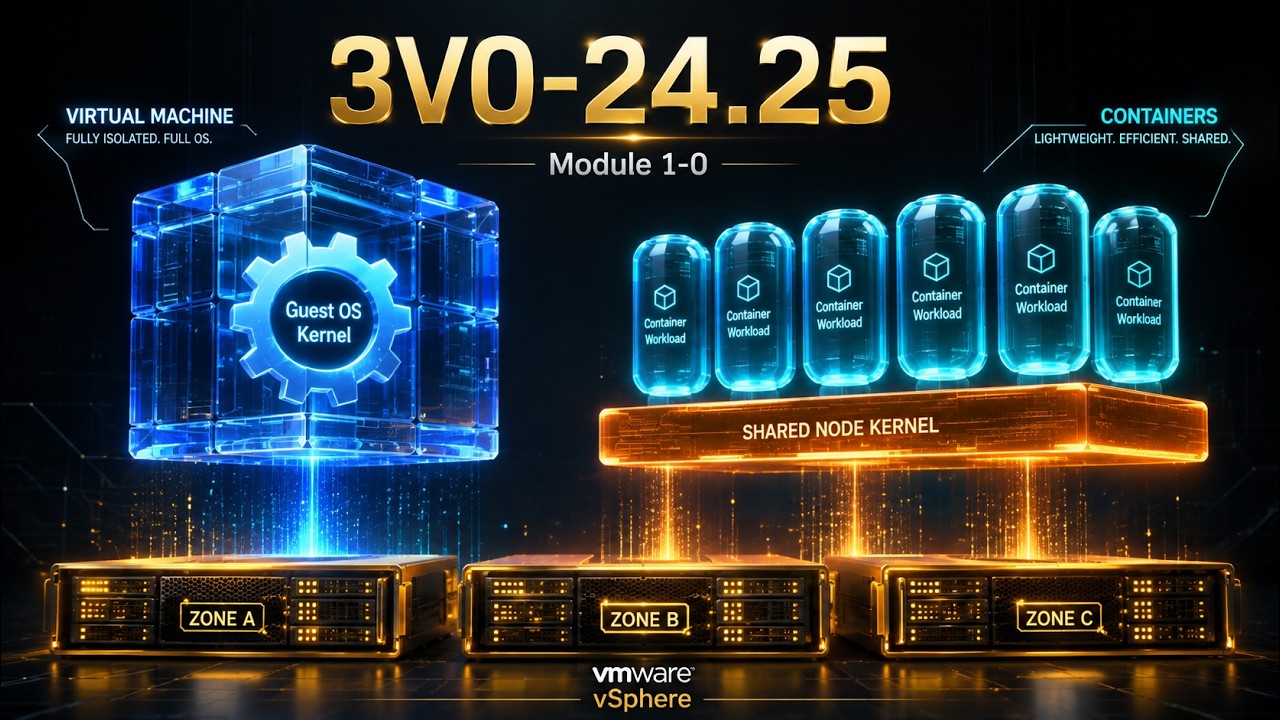
VMware VCF 9.0 Architect 3V0-24.25 Certification: VM vs Container Workload Design Explained
 6:03
Study & Preparation
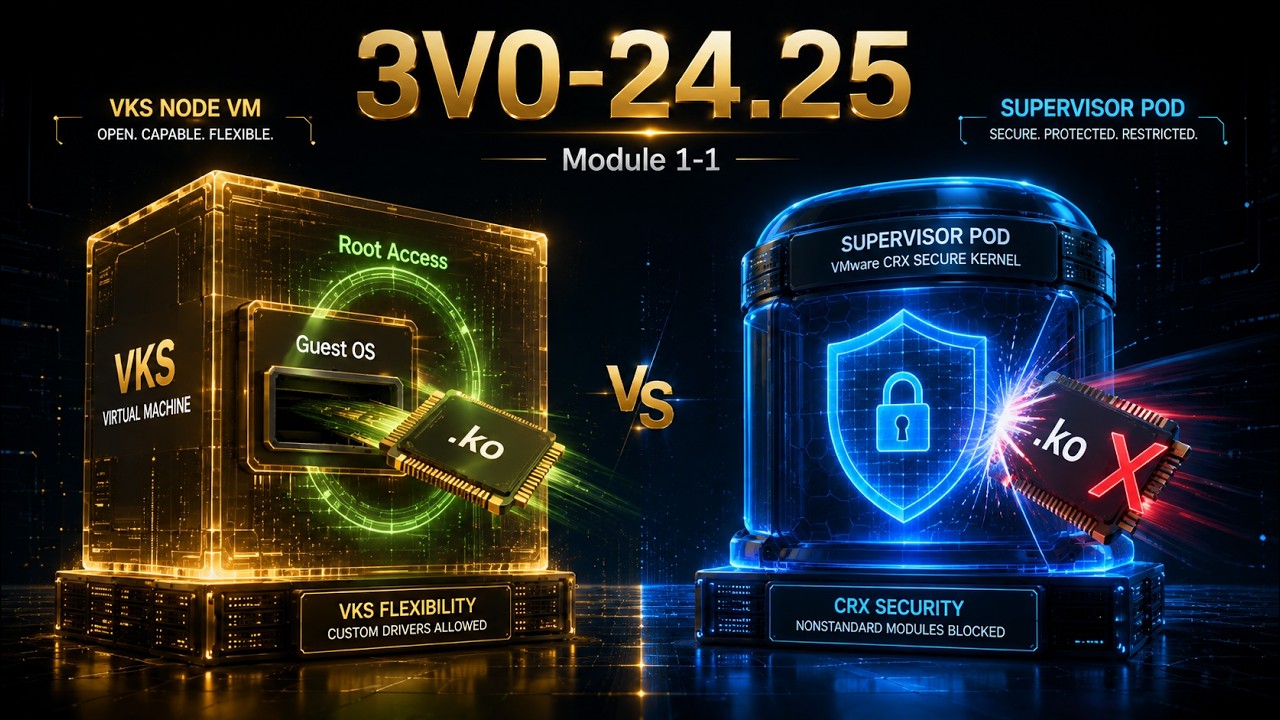
VCF 9.0 Architect 3V0-24.25 Exam: Supervisor Pods vs VKS Node VM Explained
 9:23
Study & Preparation
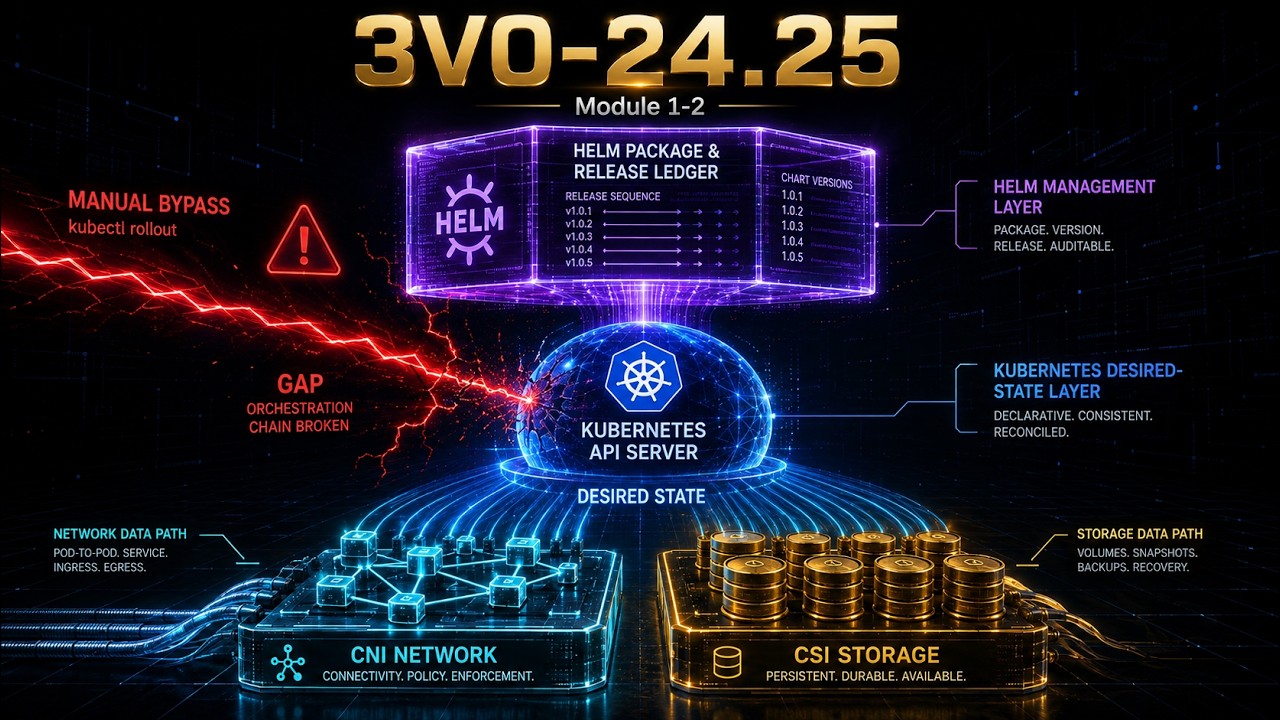
VCF 9.0 Architect 3V0-24.25 Exam: Helm and Kubernetes Troubleshooting Explained
 7:45
Study & Preparation
VCF 9.0 Architect 3V0-24.25 Exam: NSX VPC vs VDS Supervisor Architecture Explained
 8:47
Study & Preparation
VCF 9.0 Architect 3V0-24.25 Exam: Namespace Network Options Explained
 8:24
Study & Preparation