
Study & Preparation
3V0-24.25 Exam VCF 9.0 Security Architecture Explained: OIDC, RBAC, Antrea CNI and Istio Mesh
About this video
3V0-24.25 exam Security in VCF 9.0 is not a single feature — it is a layered architecture. In this video, we break down Module 5 security concepts for the VCF 9.0 Architect Exam, focusing on the boundaries between authentication, authorization, network isolation, certificate trust, and service mesh security. You will learn how OIDC authentication works with Kubernetes RBAC, why successful login can still result in a 403 Forbidden error, how Antrea CNI and NSX security policies enforce micro-segmentation, and why certificate trust issues can block secure registry communication. We will also explore Istio service mesh concepts, including mTLS, Sidecar mode, Ambient mode, ztunnel, and waypoint components — and how these technologies fit into a modern zero-trust Kubernetes architecture. The exam is not testing whether you can remember individual commands. It is testing whether you understand how each security layer interacts and where failures actually occur. By the end of this module overview, you will have a clearer mental model for analyzing VCF security scenarios and avoiding the common architecture mistakes that confuse many candidates. Next, we will move into hands-on identity federation and RBAC configuration to understand how least-privilege access is implemented in practice. #VCF9 #VMware #VKS
Keep watching
 7:07
Study & Preparation
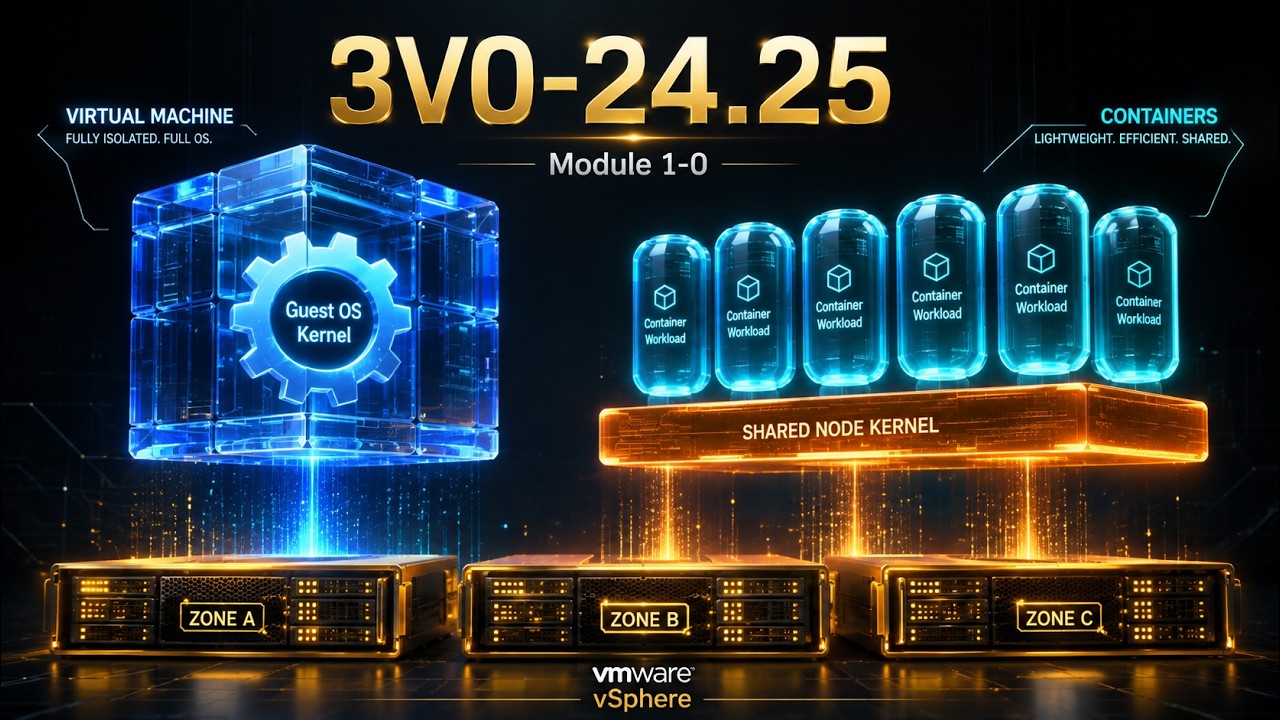
VMware VCF 9.0 Architect 3V0-24.25 Certification: VM vs Container Workload Design Explained
 6:03
Study & Preparation
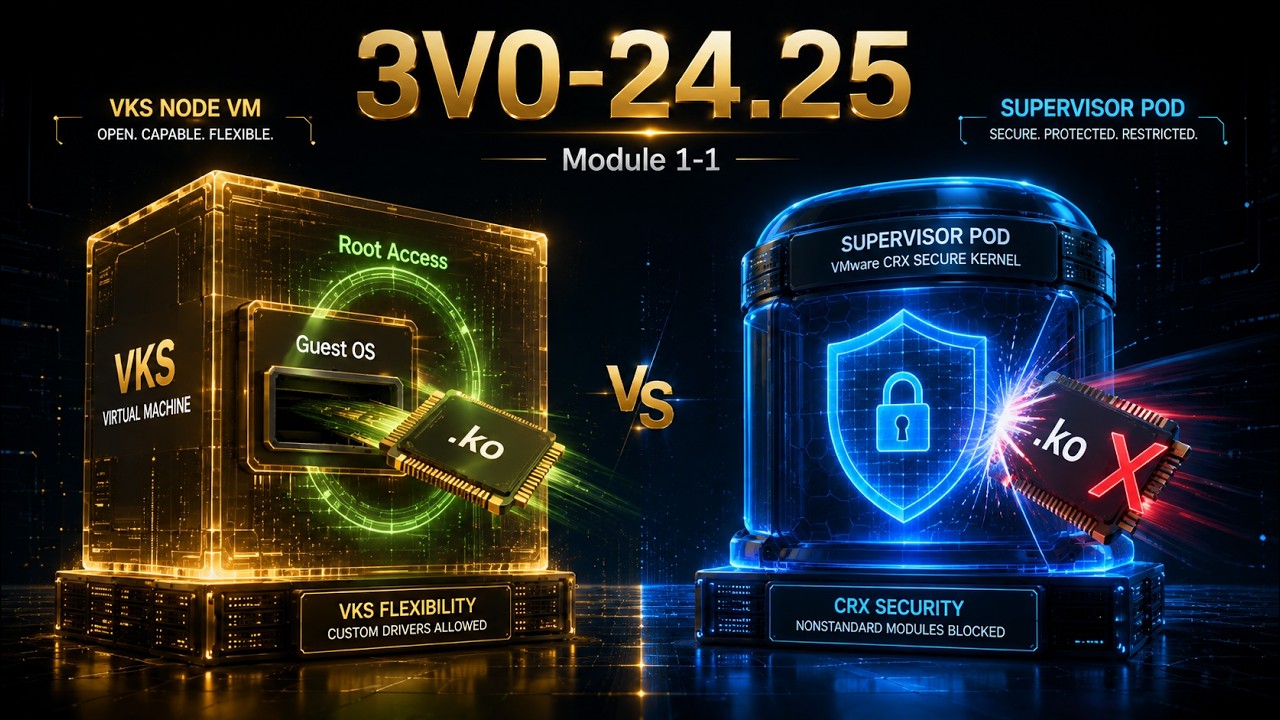
VCF 9.0 Architect 3V0-24.25 Exam: Supervisor Pods vs VKS Node VM Explained
 9:23
Study & Preparation
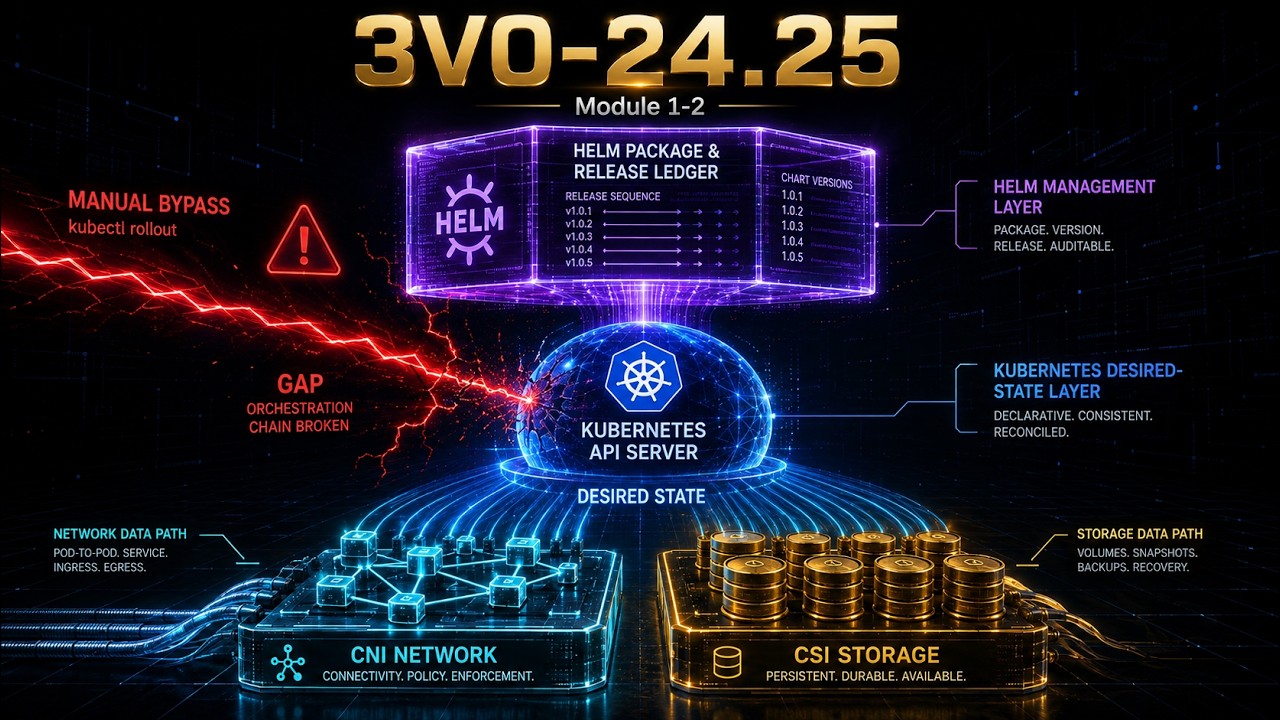
VCF 9.0 Architect 3V0-24.25 Exam: Helm and Kubernetes Troubleshooting Explained
 7:45
Study & Preparation
VCF 9.0 Architect 3V0-24.25 Exam: NSX VPC vs VDS Supervisor Architecture Explained
 8:47
Study & Preparation
VCF 9.0 Architect 3V0-24.25 Exam: Namespace Network Options Explained
 8:24
Study & Preparation