
Study & Preparation
3V0-24.25 Istio Service Mesh: Sidecar, Ambient Mode and Strict mTLS
About this video
Installing Istio is only the beginning. A healthy service-mesh control plane does not automatically prove that your application workloads are participating in the data plane. That distinction is where many 3V0-24.25 service-mesh scenarios become difficult. In this video, we break down Objective 3.6 of the VMware VKS exam and examine the correct sequence for implementing Istio: deploy the package, choose the data-plane architecture, enroll the workloads, verify traffic capture, and then enforce Strict mTLS. Broadcom’s official exam guide specifically includes service-mesh implementation under Objective 3.6. We will compare Istio’s two primary data-plane models: Sidecar mode, where an Envoy proxy runs alongside each application Pod Ambient mode, where node-level ztunnel components provide Layer 4 security and optional waypoint proxies add Layer 7 processing Sidecar enrollment requires existing Pods to be recreated before the proxy can be injected. Ambient mode provides transparent namespace enrollment and normally does not require application Pods to restart. We will also examine why applying Strict mTLS at the wrong stage can interrupt application communication. Strict mode allows protected workloads to accept only authenticated mTLS traffic, so requests arriving from outside the mesh can be rejected even when basic Kubernetes networking is working correctly. The practical verification workflow covers: Confirming the Istio add-on installation Checking control-plane and ztunnel readiness Verifying namespace enrollment labels Confirming Envoy injection in Sidecar mode Validating Ambient mode capture Testing secure service-to-service communication The 3V0-24.25 exam is not simply testing whether you recognize an Istio command. It is testing whether you can separate package readiness from data-plane readiness and apply security policies in an operationally safe order. By the end of this module, you will have a clearer troubleshooting model for Sidecar injection, Ambient enrollment, ztunnel, waypoint proxies, and Strict mTLS enforcement in a VKS environment. Next, we will configure external Layer 7 access using Istio gateways, Kubernetes Gateway API resources, and HTTPRoute policies. #3V02425 #VKS #VMwareCertification
Keep watching
 7:07
Study & Preparation
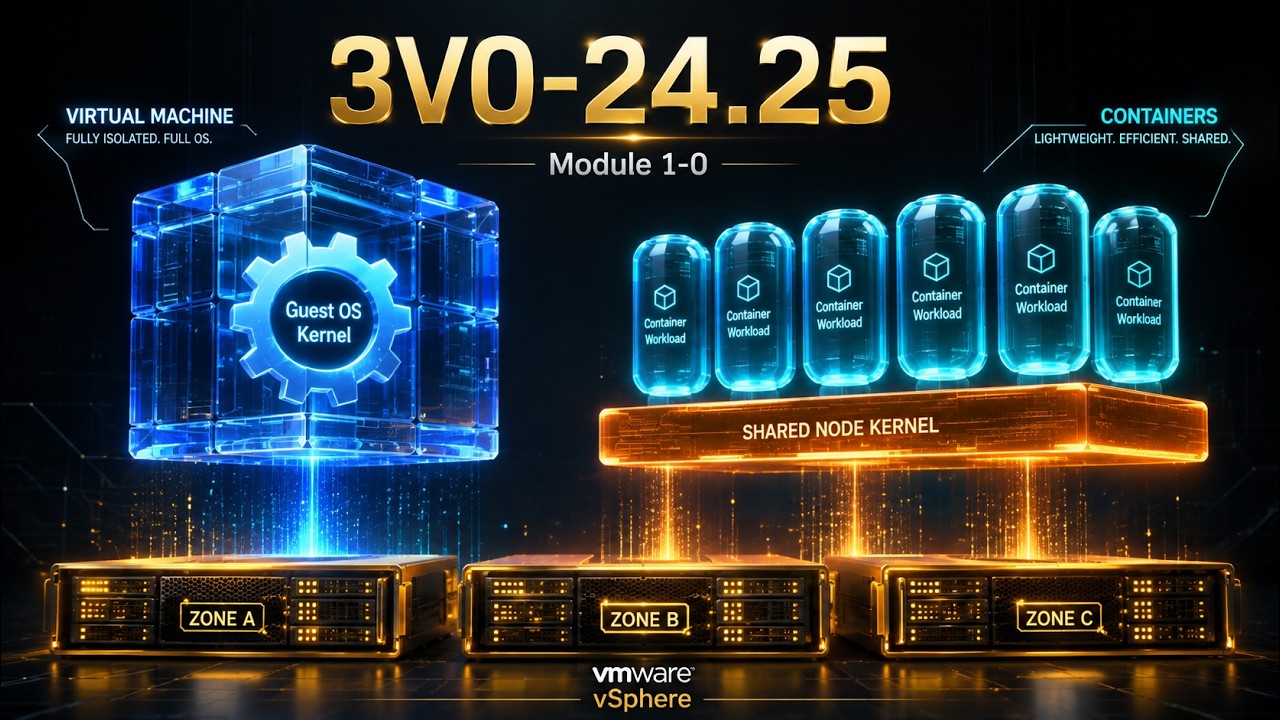
VMware VCF 9.0 Architect 3V0-24.25 Certification: VM vs Container Workload Design Explained
 6:03
Study & Preparation
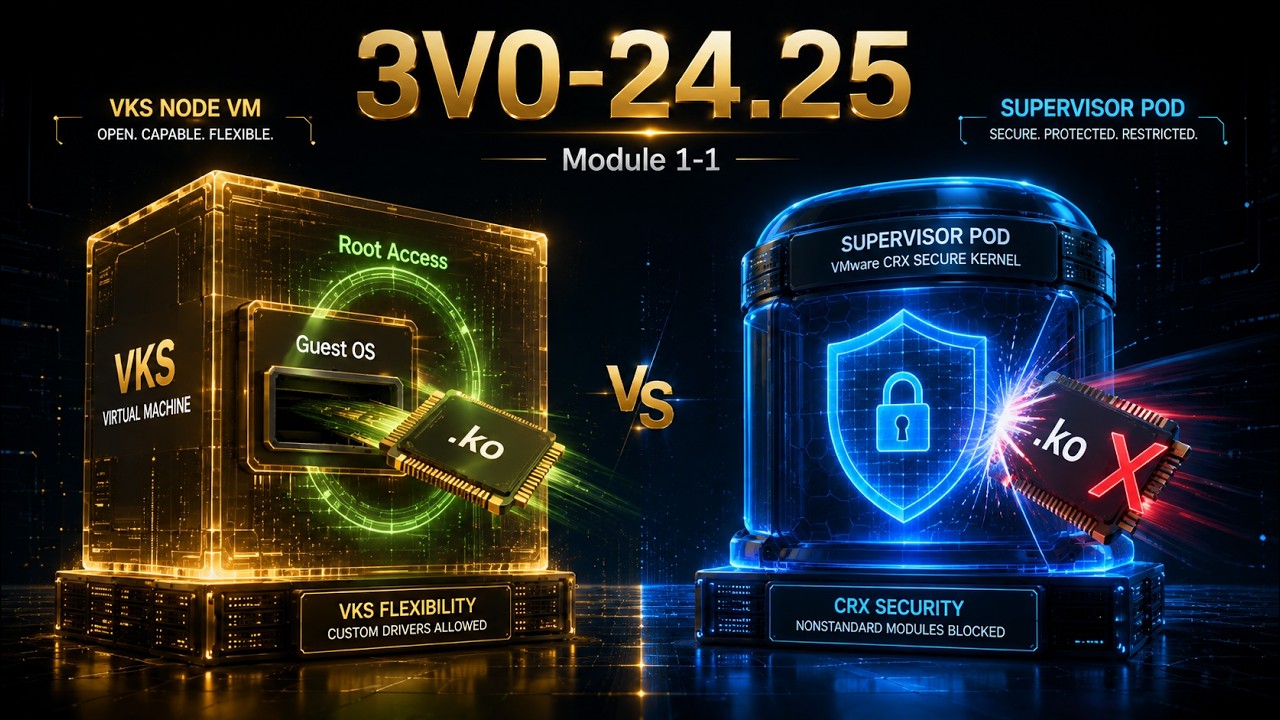
VCF 9.0 Architect 3V0-24.25 Exam: Supervisor Pods vs VKS Node VM Explained
 9:23
Study & Preparation
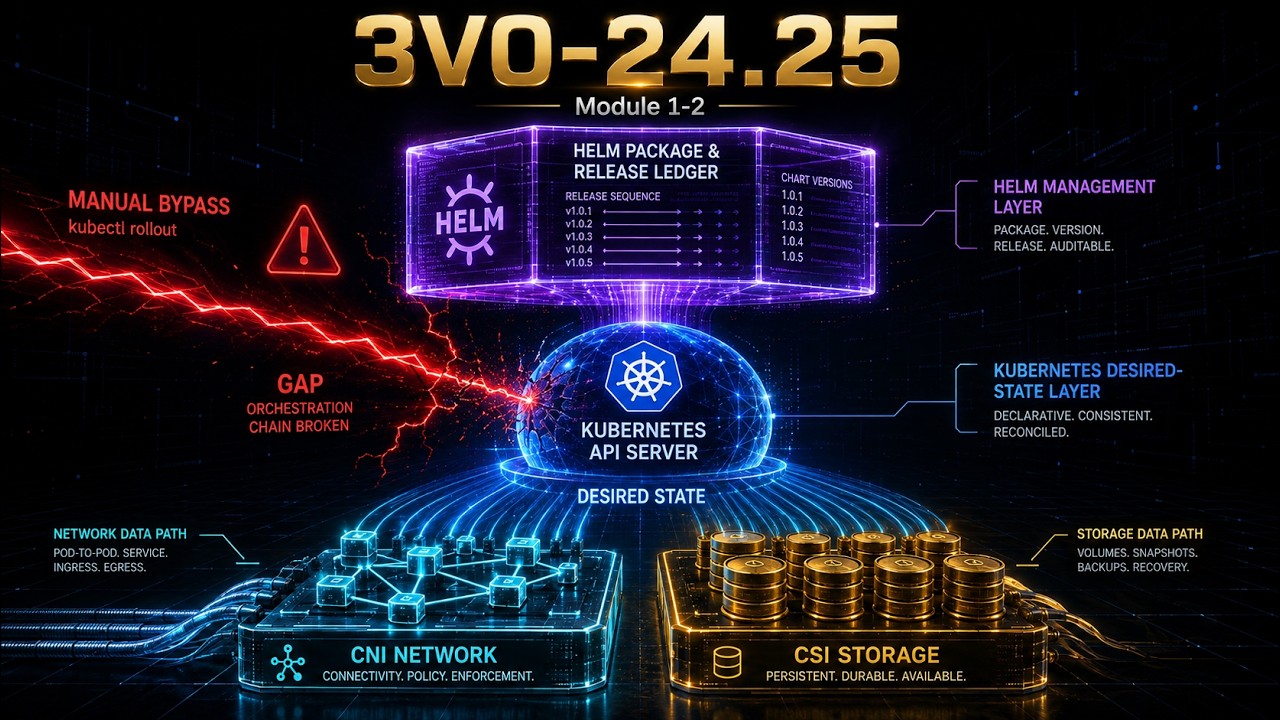
VCF 9.0 Architect 3V0-24.25 Exam: Helm and Kubernetes Troubleshooting Explained
 7:45
Study & Preparation
VCF 9.0 Architect 3V0-24.25 Exam: NSX VPC vs VDS Supervisor Architecture Explained
 8:47
Study & Preparation
VCF 9.0 Architect 3V0-24.25 Exam: Namespace Network Options Explained
 8:24
Study & Preparation